Monday, June 6, 2011

How To Install Or Upgrade LAMP: Linux, Apache, MySQL and PHP Stack Using Yum

Installing LAMP stack using yum 

        is very easy and takes only minutes. This is a good option for beginners who don’t feel comfortable installing from source. Also, Installing LAMP stack using yum is a good choice, if you want to keep things simple and just use the default configuration.

1. Install Apache using Yum

Apache
# rpm -qa | grep httpd

[Note: If the above command did not return anything,
          install apache as shown below]

# yum install httpd
 
Verify that Apache got installed successfully

# rpm -qa | grep -i http

httpd-tools-2.2.9-1.fc9.i386
httpd-2.2.9-1.fc9.i386
 
Start the Apache as shown below.

# service httpd start 

Starting httpd: [ OK ]

2. Upgrade Apache using Yum

If you’ve selected web server package during Linux installation, Apache is already installed on your Linux. In which case, you can upgrade Apache to the latest version as shown below.
Check whether Apache is already installed.

# rpm -qa | grep -i http 

httpd-tools-2.2.8-3.i386 httpd-2.2.8-3.i386


Check whether latest version of Apache is available for installation using yum. 

yum check-update httpd
Loaded plugins: refresh-packagekit
 
httpd.i386      2.2.9-1.fc9       updates
 
[Note: This indicates that the latest Apache version 2.2.9
       is available for upgrade]

Upgrade Apache to latest version using yum.
 
# yum update httpd


Verify whether the Apache got upgraded successfully.
 
# rpm -qa | grep -i http

httpd-tools-2.2.9-1.fc9.i386
httpd-2.2.9-1.fc9.i386
[Note: This indicates that Apache was upgraded to 2.2.9 successfully]

3. Install MySQL using Yum

MySQL Logo
  Yum is very smart to identify all the dependencies and install those automatically. For example, while installing mysql-server using yum, it also automatically installs the depended mysql-libs, perl-DBI, mysql, perl-DBD-MySQL packages as shown below.
 
# yum install mysql-server


Verify whether MySQL got installed properly.

# rpm -qa | grep -i mysql

php-mysql-5.2.6-2.fc9.i386
mysql-libs-5.0.51a-1.fc9.i386
mysql-server-5.0.51a-1.fc9.i386
perl-DBD-MySQL-4.005-8.fc9.i386
mysql-5.0.51a-1.fc9.i386

# mysql -V

mysql  Ver 14.12 Distrib 5.0.51a, for redhat-linux-gnu (i386) using readline 5.0

Configure MySQL to start automatically during system startup.
 
# chkconfig mysqld on

Start MySQL service.
 
# service mysqld start

     The first time when you start mysqld, it will give additional information message indicating to perform post-install configuration as shown below.
 
Initializing MySQL database:
Installing MySQL system tables... OK
Filling help tables... OK

To start mysqld at boot time you have to copy
support-files/mysql.server to the right place for your system

PLEASE REMEMBER TO SET A PASSWORD FOR THE MySQL root USER !
To do so, start the server, then issue the following commands:
 
/usr/bin/mysqladmin -u root password 'new-password'
/usr/bin/mysqladmin -u root -h dev-db password 'new-password'

Alternatively you can run: /usr/bin/mysql_secure_installation 
which will also give you the option of removing the test
databases and anonymous user created by default.  This is
highly recommended for production servers.
See the manual for more instructions.
You can start the MySQL daemon with:
cd /usr ; /usr/bin/mysqld_safe &
You can test the MySQL daemon with mysql-test-run.pl
cd mysql-test ; perl mysql-test-run.pl
Please report any problems with the /usr/bin/mysqlbug script!
The latest information about MySQL is available on the web at

http://www.mysql.com

Support MySQL by buying support/licenses at http://shop.mysql.com

Starting MySQL:                                            [  OK  ]

4. Perform MySQL post-installation activities

After the mysql installation, you can login to mysql root account without providing any password as shown below.
 
# mysql -u root

Welcome to the MySQL monitor.  Commands end with ; or \g.
Your MySQL connection id is 2
Server version: 5.0.51a Source distribution

Type 'help;' or '\h' for help. Type '\c' to clear the buffer.

mysql>

     To fix this problem, you need to assign a password to mysql root account as shown below. Execute mysql_secure_installation script, which performs the following activities:
  • Assign the root password
  • Remove the anonymous user
  • Disallow root login from remote machines
  • Remove the default sample test database
 
# /usr/bin/mysql_secure_installation

Output of mysql_secure_installation script:
NOTE: RUNNING ALL PARTS OF THIS SCRIPT IS RECOMMENDED FOR ALL MySQL
SERVERS IN PRODUCTION USE!  PLEASE READ EACH STEP CAREFULLY!

In order to log into MySQL to secure it, we'll need the current
password for the root user.  If you've just installed MySQL, and
you haven't set the root password yet, the password will be blank,
so you should just press enter here.

Enter current password for root (enter for none):
OK, successfully used password, moving on...

Setting the root password ensures that nobody can log into the MySQL
root user without the proper authorisation.

Set root password? [Y/n] Y
New password: [Note: Enter the mysql root password here]
Re-enter new password:
Password updated successfully!
Reloading privilege tables..
... Success!

By default, a MySQL installation has an anonymous user, allowing anyone
to log into MySQL without having to have a user account created for
them.  This is intended only for testing, and to make the installation
go a bit smoother.  You should remove them before moving into a
production environment.

Remove anonymous users? [Y/n] Y
... Success!

Normally, root should only be allowed to connect from 'localhost'.  This
ensures that someone cannot guess at the root password from the network.

Disallow root login remotely? [Y/n] Y
... Success!

By default, MySQL comes with a database named 'test' that anyone can
access.  This is also intended only for testing, and should be removed
before moving into a production environment.

Remove test database and access to it? [Y/n] Y
- Dropping test database...
... Success!
- Removing privileges on test database...
... Success!

Reloading the privilege tables will ensure that all changes made so far
will take effect immediately.

Reload privilege tables now? [Y/n] Y
... Success!

Cleaning up...
All done!  If you've completed all of the above steps, your MySQL
installation should now be secure.
Thanks for using MySQL!

Verify the MySQL post-install activities:
 
# mysql -u root

ERROR 1045 (28000):Access denied for user 'root'@'localhost'(using password:NO)
[Note: root access without password is denied]

# mysql -u root -p

Enter password:
Welcome to the MySQL monitor.  Commands end with ; or \g.
Your MySQL connection id is 13
Server version: 5.0.51a Source distribution

Type 'help;' or '\h' for help. Type '\c' to clear the buffer.

mysql> show databases;
+--------------------+
| Database           |
+--------------------+
| information_schema |
| mysql              |
+--------------------+
2 rows in set (0.00 sec)
[Note: test database is removed]

5. Upgrade MySQL using Yum

Check whether MySQL is already installed.

# rpm -qa | grep -i mysql

Check whether a latest version of MySQL is available for installation using yum.

# yum check-update mysql-server

Upgrade MySQL to latest version using yum.

# yum update mysql-server

6. Install PHP using Yum

PHP Logo
# yum install php

Install MySQL module for PHP.

 
# yum search php-mysql

# yum install php-mysql

If you need additional PHP modules, install them using yum as shown below.
 
# yum install php-common php-mbstring php-mcrypt php-devel php-xml php-gd

7. Upgrade PHP using Yum

Check whether PHP is installed.

# rpm -qa | grep -i php

Check whether a latest version of PHP is available for installation using yum.
 
# yum check-update php

Upgrade PHP to the latest version using yum.
 
# yum update php

Upgrade any additional PHP modules that you’ve installed using yum.
 
# yum check-update php-common php-mbstring php-mcrypt php-devel php-xml php-gd

# yum update php-common php-mbstring php-mcrypt php-devel php-xml php-gd

Verify the PHP installation by creating a test.php file as shown below.
 
# cat /var/www/html/test.php

<? phpinfo(); ?>
Invoke the test.php from the browser http://{lamp-server-ip}/test.php , which will display all PHP configuration information and the installed modules.
 

Wednesday, April 27, 2011

Linux Mail Server Setup and Howto Guide

This website will show you how to setup an email server accessible using a POP3, IMAP or web browser client. It will also show you how to include virus scanning and spam tagging in the mail server. If you have an existing Active Directory or LDAP infrastructure, the last section will show you how to integrate it into your email server so you won’t have to maintain two sets of user accounts.

The link is

http://www.linuxmail.info/

Thursday, March 31, 2011

Doing pxe boot of windows 2003

install server 2003

configure the   i) dns server
                      ii)dhcp server and create a scope


Configure the RIS Service


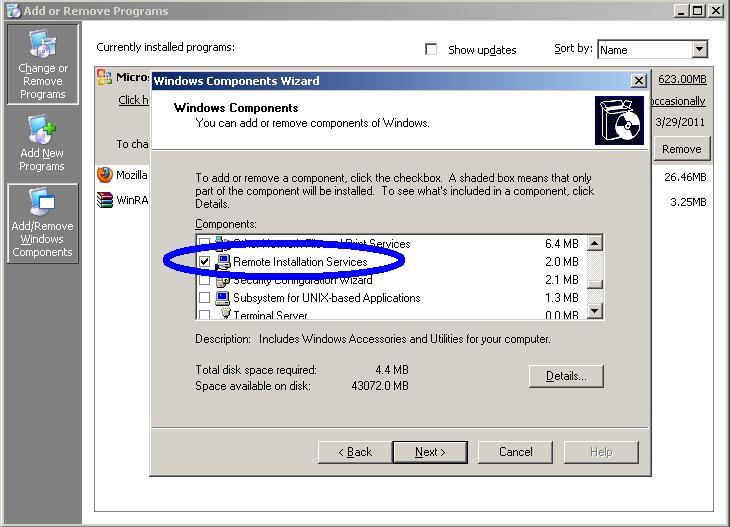
Goto start->Control panel->Add or Remove programs->Add/Remove Windows Components Select Remote Installation Service and copy files from  cd( which u want to install in the client system)


Copying the image to the RemoteInstall folder

Goto start-> Administrator tools-> Remote Installation Service setup copy the image that which u want to install in the client system.


Give the full Authentication to the RemoteInstall folder(Right click the RemoteInstall folder where u created)

 The Remote install folder should not be the System drive


DHCP server configuration

Create a scope if scope does not exists.

Goto start->Administrative tools -> DHCP  Right click DHCP Add server then select this server option then the dhcp server will be created with domain name Right Click and select New scope and create a new scope then scope will be created.

Double click on scope ->scope options -> Right click configure options then

                                           configure these options i) Router
                                                                               ii)Boot server hostname
                                                                               iii)Bootfile name


Adding the Network driver to the RIS image


                 Create the directory  shown below inside the  drive:\RemoteInstall\Setup\English\Images\WINDOWS\i386

                                    \$oem$\$1\Drivers\Nic

Download the oem network driver from below url:


http://drivers.brothersoft.com/realtek-ethernet-pci-e-driver-5.776-for-2003-xp-download-47037.html

Copy the downloaded driver into the below path


Drive:\RemoteInstall\Setup\English\Images\WINDOWS\i386\$oem$\$1\Drivers\Nic\  


In Regedit(registry) HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Current Version\devicePath default will be %Systemdrive%\inf change into

            Drive:\RemoteInstall\Setup\English\Images\WINDOWS\i386\$oem$\$1\Drivers\Nic\

      then restart u r computer and boot the client system through network.


Requirements for the client system

The system should be connected to the network.

Red Hat 6: How to boot into Single-user mode

There are a few situations where we need to take a Linux system actually offline:
  • file systems operations ( i.e. resizing, backup/restore, fsck)
  • general maintenance (certain things simply cannot be done in multi-user mode)
  • lost root passwords (often enough a single admin is around, typically not documenting changes etc., or disgrantled employees do some harm )
In such situations, it is necessary to boot into Single-user mode (aka runlevel 1).
There are basically 2 general ways of achieving this:
  1. If you have a valid login account with elevated permissions, and want to do some maintenance, just change the runlevel as described here.
  2. If you lost the root password, you must reboot the computer and edit the bootloader ( typically GRUB) to boot into Single user mode.
In a situation where the root password is already lost and no other account with equivalent permissions is available, you probably have to hard-reset the system.
If that is a physical server, you might have to press the power button typically for 4 seconds or longer, or even unplug the power  cable, as most if not all modern servers can be configured on BIOS level to ignore the power buttons. Many companies  have coded this in their policies to ensure important servers are not being switched off by coincidence.
To reset a physical server, you usually need to have also physical access to that very box, including keyboard and monitor, or via KVM switch if available.
A virtual machine can usually be reset a bit easier, depending on the host system (VMware, XEN, KVM, etc. etc.).
Either way, once your system is rebooting, you need to access the edit bootloader, which in Redhat 6 is GRUB (GRand Unified Bootloader).
When the screen shows the GRUB stage 1, it counts down 4 seconds (at least per default configuration, this can be different in many cases) with one head-line “Press any key to enter the menu” and printing another line every second, stating which kernel will be booted:
GRUB stage 1
Press any key here to get into the GRUB menu:
GRUB stage2 menu
Good job! As you can see in the text under the border, you have a few choices now:
  • use the cursor keys to switch between kernels (if you have more than 1 installed) to chose the one you want to boot
  • press “enter ” to boot the selected kernel
  • press “e” to edit the kernel commands before booting => this will be our choice
  • press “a” to modify the kernel arguments
  • press “c” to go to a command-line,  for extended troubleshooting etc.
One you pressed “e” while the kernel of your choice is highlighted, you get a second menu:
GRUB stage 2 menu 2
Here it is vital to highlight the second line ( while it is possible to edit parameters on each of the lines, the second line is just where we need to go),  and press “e” once more to edit:
GRUB stage 2 menu3
Here we simply type the word “single” at the end of the line to add one more argument to the kernel:
add "single"
(Note that there are quite a few more parameters available to add, but we want to get into single-user mode so that is all we need for now).
Make sure to hit “enter” to actually add the argument and to return to the boot menu. Escape does get you back to the same menu as well, but it does not add the argument, so your work will be undone actually.
Grub stage 2 menu3
We are back to the previous menu, and if you like you can press “e” again to ensure that “single” is now added to the end of the line, otherwise you just can hit “b” now to boot into single-user mode:
single-user mode
As you can see at the bottom of the screen, you are now logged on as root without having to present any credentials. If you came here to reset your root password, just type passwd to do so:
[root@your_system /]# passwd
and enter the password of your choice when prompted.
As you can see, this is actually a very easy process.  As such, please always be aware that anyone who has access to this system can do that as well! Server or workstation, both have should be always secured in one way or the other. File level encryption might be one way of securing your data, but it does probably not help against someone trying to bring your system down, i.e. DOS attacks.

Monday, March 28, 2011

How to setup multimedia on Redhat 6 & Centos (32 and 64 bit)

Step 1: 

Add RPMforge repository access for your Redhat $ CentOS system. (Required for the majority of multimedia packages.)

Installing RPMforge for Redhat 6 & Centos 6

The default RPMforge repository does not replace any CentOS base packages. In the past it used to, but those packages are now in a separate repository (rpmforge-extras) which is disabled by default.
You can find a complete listing of the RPMforge package packages at http://packages.sw.be/
Download the rpmforge-release package. Choose one of the two links below, selecting to match your host's architecture. If you are unsure of which one to use you can check your architecture with the command uname -i
        The preferred rpmforge-release package to retrieve and to install in order to enable that repository is one of the two listed above.

Install DAG's GPG key
 
rpm --import http://apt.sw.be/RPM-GPG-KEY.dag.txt


Verify the package you have downloaded
 
rpm -K rpmforge-release-0.5.2-2.el6.rf.*.rpm

Install the package
 
rpm -i rpmforge-release-0.5.2-2.el6.rf.*.rpm

This will add a yum repository config file and import the appropriate GPG keys. 

Installing Dag RPM Repository for Red Hat Enterprise Linux

     The DAG RPM repositories which contains huge amount of rpm packages. It’s very easy. Just install the latest rpmforge-release package for your distribution and architecture.

This will automatically install the configuration and GPG keys that are for safely installing RPMforge packages.

First :-

# gedit /etc/yum.repos.d/dag.repo

Insert :-

[dag]

name=Dag RPM Repository for Red Hat Enterprise Linux
baseurl=http://apt.sw.be/redhat/el6/en/x86_64/dag/
gpgcheck=1
enabled=1

Then save the repo file also you can update RPM

Find out waht the actual name for missing package from this site:

http://pkgs.org/

Download the package from this site

http://ftp.redhat.com/redhat/rhel/beta/6/optional/x86_64/os/Packages/


Step 2: Install the multimedia applications.

 
The following steps will use yum to install all the packages needed to have full multimedia support. Note there will be a lot of dependencies.
yum install compat-libstdc++-33 libdvdcss libdvdread libdvdplay libdvdnav lsdvd libquicktime
yum install flash-plugin mplayerplug-in mplayer mplayer-gui gstreamer-ffmpeg gstreamer-plugins-bad gstreamer-plugins-ugly


Step 3: Install the w32Codecs. (Required for xvid and other proprietary formats.)
 
wget www1.mplayerhq.hu/MPlayer/releases/codecs/mplayer-codecs-20061022-1.i386.rpm
rpm -ivh mplayer-codecs-20061022-1.i386.rpm
wget www1.mplayerhq.hu/MPlayer/releases/codecs/mplayer-codecs-extra-20061022-1.i386.rpm
rpm -ivh mplayer-codecs-extra-20061022-1.i386.rpm    

Redhat 6 Beta Package (32 and 64 bit)

Download Beta RPM in this site


http://ftp.redhat.com/redhat/rhel/beta/6/optional/x86_64/os/Packages/

Tuesday, March 22, 2011

Install Google Chrome with YUM on Fedora 14/13, Red Hat (RHEL) 6

This howto explains howto install Google Chrome Web browser on Fedora 14, Fedora 13, Fedora 12 and Red Hat 6 (RHEL 6). Best way to install and keep up-to-date with Google Chrome browser is use Google’s own YUM repository.

Enable Google YUM repository

Add following to /etc/yum.repos.d/google.repo file:

32-bit


[google]
name=Google - i386
baseurl=http://dl.google.com/linux/rpm/stable/i386
enabled=1
gpgcheck=1
gpgkey=https://dl-ssl.google.com/linux/linux_signing_key.pub


64-bit
 
[google64]
name=Google - x86_64
baseurl=http://dl.google.com/linux/rpm/stable/x86_64
enabled=1
gpgcheck=1
gpgkey=https://dl-ssl.google.com/linux/linux_signing_key.pub


Note: Both 32-bit and 64-bit repos can be placed in the same file.

Install Google Chrome with YUM (as root user)

Install Google Chrome Stable Version

## Install Google Chrome Stable version ##
yum install google-chrome-stable

Install Google Chrome Beta Version

## Install Google Chrome Beta version ##
yum install google-chrome-beta

Install Google Chrome Unstable Version

## Install Google Chrome Unstable version ##
yum install google-chrome-unstable